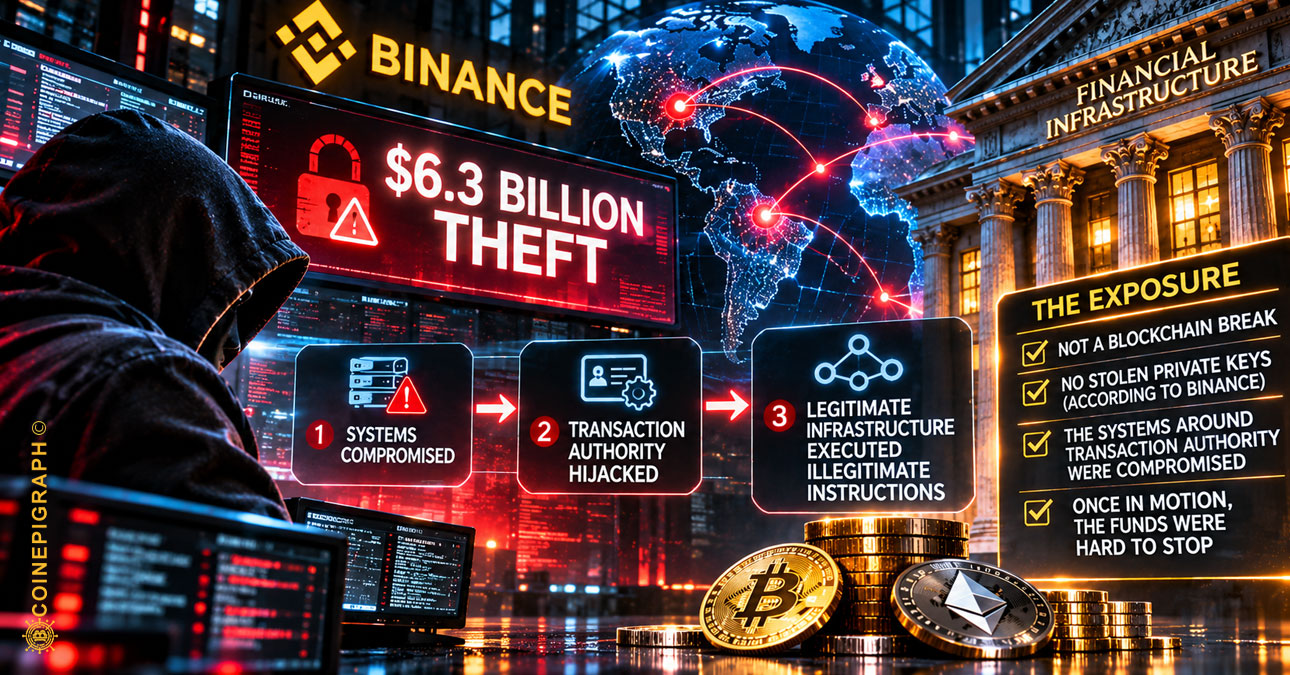
Attackers did not need to break a blockchain or, according to Binance, steal its wallet private keys to move more than $6 billion in digital assets. They compromised the systems surrounding transaction authority, then exposed how difficult it can be to stop money once legitimate financial infrastructure begins obeying illegitimate instructions.
By CoinEpigraph Editorial Desk
The most important fact about the $6.3 billion theft from Binance may be what the attackers apparently did not steal.
The private keys.
Binance says its investigation has found no evidence that the private keys protecting the affected wallets were compromised. Instead, the attackers penetrated infrastructure surrounding the wallets: employee devices, credentials, an internal AI tool, deployment permissions and eventually an internal wallet-signing service capable of authorizing transactions.
That distinction changes the meaning of the attack.
For years, digital-asset security has been organized around a relatively intuitive proposition. Protect the key and you protect the money.
The Binance breach demonstrated the limits of that model.
A financial system can protect the cryptographic secret at its center and still lose control of billions of dollars if an attacker gains sufficient authority over the machinery allowed to instruct it.
The attack therefore belongs to a larger category than cryptocurrency theft.
It was an attack on financial authorization infrastructure.
The Key Wasn’t Enough
On October 29, funds began leaving Binance hot wallets across several blockchain networks.
The attack moved quickly.
Binance’s post-incident report describes unauthorized transfers involving XRP, SOL, OP and Bitcoin before the attackers turned to Ethereum and used the exchange’s compromised signing infrastructure to establish malicious authorizations under Ethereum’s EIP-7702 mechanism.
The sequence matters.
EIP-7702 was designed to make ordinary Ethereum accounts more programmable. Among other capabilities, it allows an externally owned account to delegate execution rights to smart-contract code without surrendering the account’s private key.
That can enable useful functionality.
It can also make authorization itself more consequential.
According to Binance, the attackers submitted 50 signing transactions that manipulated account nonces and established malicious delegation authorizations. Once those permissions existed on-chain, the attack acquired a characteristic that complicated Binance’s response.
The permissions no longer depended on the exchange’s normal withdrawal system.
Binance suspended withdrawals.
The malicious authority remained.
It shut down affected hot-wallet services.
The malicious authority remained.
The exchange then had to revoke the authorizations separately on-chain.
The distinction is subtle but fundamental.
Stopping the normal mechanism for moving money did not necessarily stop authority that had already been established somewhere else.
That is not merely a Binance problem.
Programmable finance increasingly allows financial authority to persist in software.
Security architecture has to account for that.
The Attack Moved Through People Before It Moved Through Wallets
The technical sophistication of the Ethereum transactions can obscure how the attack began.
Binance describes a multi-stage campaign involving fake recruitment interviews, malicious software, compromised endpoints and stolen credentials.
An engineer’s computer was compromised. The attackers subsequently gained access to other employees and internal systems. Binance says an internal AI tool was among the compromised infrastructure.
Eventually the attackers reached wallet-signing operations.
This is a familiar cybersecurity pattern operating at an unfamiliar financial scale.
The blockchain did not need to be broken.
The humans did not necessarily need to understand the final attack.
The attacker needed to move through enough trusted systems until reaching one capable of issuing instructions that the financial infrastructure would accept.
That is where conventional cybersecurity and programmable finance begin to converge.
A blockchain can validate a signature.
It cannot determine whether the organization producing that signature has been socially engineered.
It can confirm that an authorization satisfies protocol rules.
It cannot know whether the institution intended to grant that authorization.
Cryptographic validity and institutional intent are not the same thing.
The Binance theft turned the gap between them into a multibillion-dollar event.
MPC Created Security—and a Different Recovery Problem
Binance’s hot-wallet architecture adds another layer.
The affected Ethereum wallet used multiparty computation, or MPC. Rather than relying on a single private key that one person or system can possess, MPC distributes the signing process.
That architecture is intended to reduce the danger associated with a single compromised key.
It appears to have done something important here: Binance says it has found no evidence that the wallet’s private key leaked.
But the incident also exposed a different operational problem.
Because there was no single private key available, Binance could not simply use one key to immediately revoke the malicious EIP-7702 delegation. It had to develop and execute a specialized procedure to remove the authorization.
Security had removed one obvious point of failure.
The attackers had found another route to authority.
That does not make MPC defective. It illustrates something more important about complex financial systems.
Every additional security layer changes the failure modes around it.
The question is no longer only whether a control prevents compromise.
It is also whether the institution can rapidly recover authority when another part of the system has already been compromised.
The Theft Continued After Withdrawals Stopped
This may be the most revealing moment in the incident.
Binance says the final unauthorized transfer—2,961.9 ETH—finalized on-chain at 23:56 UTC. Fourteen minutes later, the exchange executed a new authorization clearing the malicious delegation code from the affected hot wallet.
The transaction had been broadcast earlier and remained pending before eventually being confirmed.
The chronology demonstrates the difference between shutting a service and stopping settlement.
Once a valid transaction enters decentralized infrastructure, the institution that originated it may no longer possess a simple cancellation mechanism.
Traditional finance contains numerous intervention points.
Banks can freeze accounts. Payment processors can block transactions. Card networks can decline authorizations. Centralized ledgers can reverse certain entries before final settlement.
Public blockchain systems deliberately reduce some of those dependencies.
That characteristic is valuable when the instruction is legitimate.
It becomes unforgiving when the instruction is not.
The infrastructure does not know the difference.
Then the Rest of the Financial Stack Responded
The theft did not remain inside Binance.
It immediately moved into the broader digital-asset financial system.
Stablecoin issuers, exchanges, blockchain intelligence companies and law-enforcement agencies began identifying and freezing assets.
By November 3, Binance said approximately $2.85 billion of the $6.34 billion affected had been frozen or intercepted.
Chainalysis reported that freezes began within roughly an hour of the theft. It also observed the attackers converting hundreds of millions of dollars in stablecoins into Ether as they attempted to stay ahead of those interventions.
That behavior reveals another important division inside digital finance.
Not all digital assets carry the same intervention architecture.
Some stablecoins have issuers capable of freezing specific addresses or assets under certain circumstances.
Ether does not have an issuer with equivalent authority.
Bitcoin does not have one either.
For an attacker attempting to preserve control over stolen value, that difference matters.
The laundering strategy therefore became partly a race between two kinds of financial infrastructure: assets carrying centralized intervention mechanisms and assets designed to operate without them.
The attackers understood the distinction.
So did the defenders.
DeFi Became Infrastructure, Not the Breach
Aave provides another useful example.
Shortly after the theft, an address identified by Aave risk contributors as part of the exploiter’s wallet cluster supplied approximately 60 million USDT to Aave V3 on Ethereum and borrowed 19,762 WETH.
Aave was not the system that had been compromised.
Its lending infrastructure was being used after the compromise occurred elsewhere.
That distinction matters because large financial incidents increasingly move across institutional boundaries.
A centralized exchange can be breached.
The stolen assets can move onto public blockchains.
Stablecoins can encounter issuer controls.
Decentralized exchanges can provide conversion.
A lending protocol can provide collateralized liquidity.
Analytics companies can trace the flows.
Law enforcement can identify addresses.
The event may begin inside one company while the response unfolds across an entire financial ecosystem.
That makes infrastructure risk harder to assign to a single institution.
The attack path and the recovery path can travel through completely different systems.
The Money Was Programmable in Both Directions
There is a temptation to describe programmable money as either inherently dangerous or inherently resilient.
The Binance incident supports neither conclusion.
Programmability helped create the attack surface when malicious authorization was established.
Programmability also helped defenders identify transactions, monitor addresses and coordinate interventions.
Stablecoin controls allowed some assets to be frozen.
Public ledgers allowed investigators to observe flows that would have been invisible inside many traditional financial systems.
Aave continued operating according to its rules while stolen assets moved through it.
Ethereum continued settling valid transactions even though Binance desperately wanted some of them stopped.
Each component did what its architecture permitted it to do.
The failure occurred in the relationship among those components and the authority controlling them.
That is why the incident should not be reduced to a blockchain-security story.
The blockchains were largely doing what they were designed to do.
The crisis was determining whether the instructions they received represented legitimate financial intent.
A $6.3 Billion Balance-Sheet Test
Binance’s ability to absorb the loss prevented the technical breach from becoming an immediate customer solvency crisis.
The exchange committed more than $6.34 billion of company resources to replenish affected assets, drawing on its Secure Asset Fund for Users, excess Futures insurance resources and corporate treasury. Binance subsequently reported that coverage of the affected assets had been completed.
That response matters.
A security failure of this scale becomes a different kind of financial event when the institution cannot replace what was stolen.
Binance could.
But that should not obscure what the event revealed.
An institution capable of absorbing a multibillion-dollar loss can protect customers from the immediate balance-sheet consequence.
It cannot make the infrastructure lesson disappear.
The next institution may have a smaller balance sheet.
The next compromised authorization system may control assets belonging to multiple financial institutions.
The next target may not be an exchange.
As tokenized securities, stablecoins, institutional custody and automated financial agents become more deeply embedded in markets, the value controlled by programmable authorization systems will increase.
So will the consequences of getting authority wrong.
Financial Security Is Moving Beyond the Vault
Financial security once had a relatively straightforward center of gravity. Protect the asset, protect the key and restrict access to both.
The Binance theft shows why that model is becoming incomplete.
The attackers appear to have worked their way through people and systems until they reached infrastructure capable of issuing legitimate-looking financial instructions. By then, the security of the private key was only one part of the problem. The environment surrounding it had acquired enough authority to put billions of dollars in motion.
That changes what institutions have to protect.
An employee’s compromised device can become a route toward a signing system. A stolen credential can open access to infrastructure that was never intended to be exposed. A programmable wallet can retain permissions after the institution’s ordinary transaction systems have been shut down. Once an authorized transaction reaches a public blockchain, the institution may have fewer opportunities to stop it than it would inside its own ledger.
None of this makes the private key less important. It means the perimeter around financial authority has become much larger than the key itself.
That perimeter will continue to expand as institutions adopt programmable wallets, tokenized assets and automated financial agents. More systems will be capable of instructing money to move, and more of those instructions will originate outside the traditional boundaries of a bank, exchange or custodian.
Binance could replace what was stolen. Another institution may not have that capacity. More importantly, reimbursement addresses the loss after the fact. It does not solve the problem the attack exposed.
The $6.3 billion theft did not require cryptography to fail. The financial machinery surrounding it had to lose control of who was permitted to give the instructions.
As finance becomes more programmable, that distinction will matter well beyond Binance. Protecting money will still require protecting the asset and the key. Increasingly, it will also require protecting the authority to tell the money where to go.
The most consequential security boundary may no longer sit around the vault. It may sit around the instruction.
At CoinEpigraph, we are committed to delivering digital-asset journalism with clarity, accuracy, and uncompromising integrity. Our editorial team works daily to provide readers with reliable, insight-driven coverage across an ever-shifting crypto and macro-financial landscape. As we continue to broaden our reporting and introduce new sections and in-depth op-eds, our mission remains unchanged: to be your trusted, authoritative source for the world of crypto and emerging finance.
— Ian Mayzberg, Editor-in-Chief
The team at CoinEpigraph.com is committed to independent analysis and a clear view of the evolving digital asset order.
To help sustain our work and editorial independence, we would appreciate your support of any amount of the tokens listed below. Support independent journalism:
BTC: 3NM7AAdxxaJ7jUhZ2nyfgcheWkrquvCzRm
SOL: HxeMhsyDvdv9dqEoBPpFtR46iVfbjrAicBDDjtEvJp7n
ETH: 0x3ab8bdce82439a73ca808a160ef94623275b5c0a
XRP: rLHzPsX6oXkzU2qL12kHCH8G8cnZv1rBJh TAG – 1068637374
SUI – 0xb21b61330caaa90dedc68b866c48abbf5c61b84644c45beea6a424b54f162d0c
and through our Support Page.
🔍 Disclaimer: CoinEpigraph is for entertainment and information, not investment advice. Markets are volatile — always conduct your own research.
COINEPIGRAPH™ does not offer investment advice. Always conduct thorough research before making any market decisions regarding cryptocurrency or other asset classes. Past performance is not a reliable indicator of future outcomes. All rights reserved | 版权所有 ™ © 2024-2029.