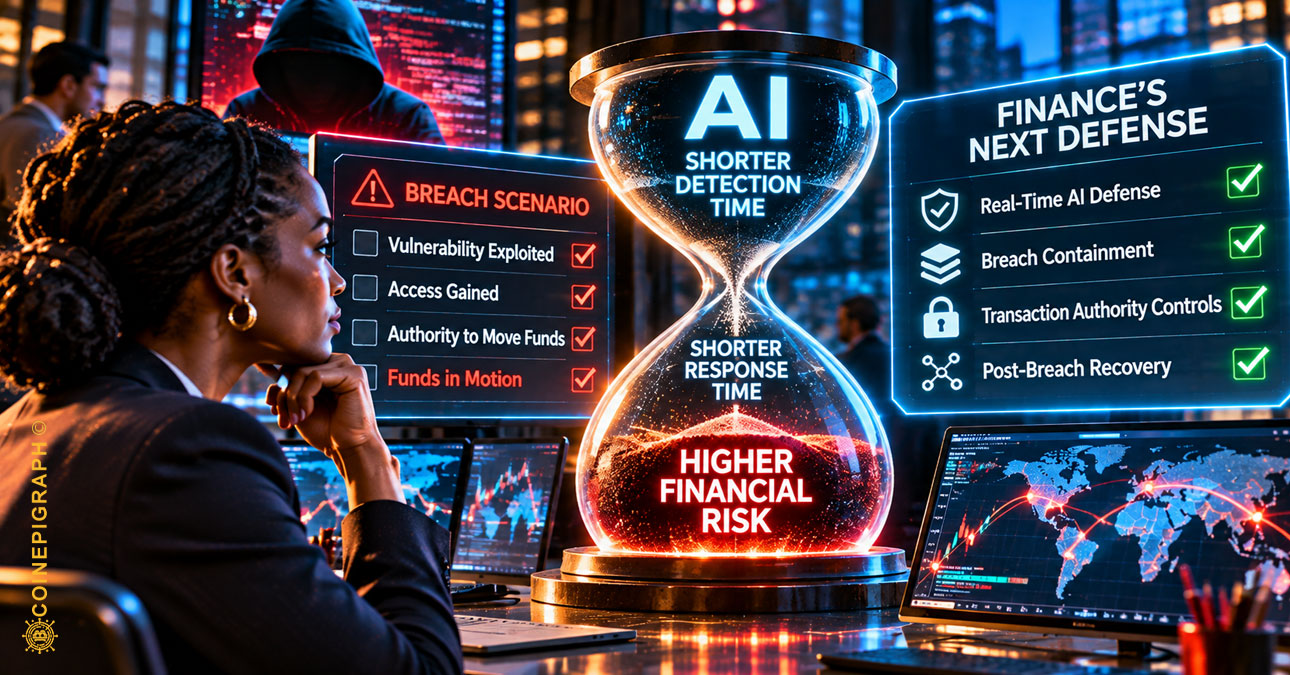
Artificial intelligence is reducing the time available to discover, repair, and respond to software vulnerabilities. For banks, exchanges, and decentralized financial systems, the harder question may be what happens after a breach—when an attacker gains the authority to move money.
By CoinEpigraph Editorial Desk
For years, financial institutions have approached cybersecurity as a contest over access.
Keep unauthorized users out. Protect credentials. Patch vulnerable software. Monitor networks for suspicious activity.
Those defenses remain essential. But artificial intelligence is changing the amount of time institutions have to make them work.
A weakness that once required an experienced researcher days to investigate may become easier to identify, test, and combine with other vulnerabilities. Defensive teams can use the same capabilities to strengthen their systems. Attackers, however, do not have to satisfy the operational requirements of a regulated financial institution before attempting an exploit.
That imbalance has attracted the attention of financial authorities.
In September, the Bank for International Settlements’ Financial Stability Institute published When Machines Attack, examining how frontier AI could compress the interval between vulnerability discovery and exploitation. The research also warned that shared software, cloud infrastructure, and AI providers could transmit disruptions across multiple institutions. Bank for International Settlements
The concern is no longer confined to whether a bank or blockchain network can keep an attacker outside its systems.
It is becoming a question of what the attacker can do after getting inside.
A Breach Is Not Yet a Financial Loss
Consider a bank employee whose credentials have been compromised.
The attacker may be able to enter an internal application, examine records, or initiate a transaction. Those are serious security failures, but they do not necessarily mean the attacker can immediately transfer an unlimited amount of money.
A bank can require additional approvals, impose transaction limits, investigate unusual beneficiaries, or intervene before a payment reaches final settlement. The effectiveness of those protections varies by institution, payment system, and circumstances.
The distinction matters.
Access to a system is one form of authority. Permission to move financial value is another.
The same distinction exists in digital-asset markets, although the mechanisms differ.
A compromised exchange administrator may have access to internal infrastructure without possessing sufficient authorization to release assets from custody. A decentralized protocol may allow a transaction to execute automatically once its contract conditions are satisfied. A wallet may require several independent signatures before funds can move.
In each case, the outcome depends on how authority has been distributed and what controls remain available when one part of the system is compromised.
This is where cybersecurity becomes financial architecture.
The Speed Problem Is Becoming Institutional
The International Monetary Fund addressed the wider risk in a June 2026 note, Artificial Intelligence and Cybersecurity in the Financial Sector.
Its central concern was not that AI would necessarily invent entirely unfamiliar forms of cyberattack. Rather, AI could increase the speed, frequency, and reach of existing techniques, allowing weaknesses in shared infrastructure to affect institutions simultaneously.
The IMF emphasized controls that restrict the damage a breach can cause, together with stronger incident response, recovery capabilities, and defensive systems capable of operating at greater speed. IMF eLibrary
That introduces a different way to evaluate security.
A firm may be highly effective at identifying malicious activity but unable to stop a transaction that settles before an alert is reviewed.
Another may experience an intrusion yet contain the financial damage because the compromised account cannot independently authorize a large transfer.
The second institution has still suffered a breach. But its financial exposure may be substantially smaller.
For risk managers, that difference can determine whether an incident becomes an operational expense, a material financial loss, or a threat to the institution’s continued operation.
It also raises a question that traditional cybersecurity measurements do not always answer: how much financial authority can any single compromised system exercise?
Why Settlement Changes the Calculation
Financial transactions are not ordinary data transfers.
Once money or securities move, the institution may face legal, contractual, technical, and operational limits on reversing the transaction.
Traditional financial systems contain multiple stages between payment initiation and final settlement. Depending on the rail, those stages can provide opportunities for fraud detection, rejection, cancellation, or recovery.
They do not guarantee that stolen money can be recovered. Some payments become final quickly, and fraudulent transfers can move through several institutions before intervention is possible.
Blockchain systems introduce a different arrangement.
A validly authorized transaction may be executed and recorded without an intermediary reviewing its commercial purpose. Once finalized, the network ordinarily does not provide a conventional chargeback mechanism.
That is valuable when participants need predictable settlement without relying on a central operator.
It becomes more complicated when the authorization itself has been compromised.
A blockchain can correctly execute a transaction that its legitimate owner never intended.
The ledger has not necessarily malfunctioned. It has followed the instructions presented to it.
This exposes a distinction between cryptographic validity and financial legitimacy.
A valid signature establishes that the required cryptographic authorization was supplied. It does not, by itself, establish that the person or institution entitled to control the assets knowingly approved the underlying transaction.
For digital finance, the security problem therefore extends beyond protecting private keys. It includes deciding how much authority a key should carry, under which conditions, and whether independent controls should intervene before exceptionally consequential transfers.
The Case for Limiting Financial Authority
Several established techniques offer ways to reduce exposure.
Multisignature arrangements can require authorization from multiple independent parties. Transaction policies can restrict destinations, asset types, or transfer amounts. Time delays can create an opportunity to investigate unusual activity before execution.
Some institutions distribute signing authority across separate environments, reducing the consequences of compromising a single machine.
None of these approaches is universally appropriate.
A time delay may be acceptable for moving substantial treasury reserves but impractical for a merchant accepting everyday payments. Multiple approvals can protect institutional assets while introducing operational bottlenecks. Emergency intervention powers may prevent losses but also create new points of centralized control.
The design challenge is to match the level of authorization to the consequences of the transaction.
A payment of a few dollars should not necessarily require the same controls as a transfer representing a substantial portion of an institution’s assets.
Nor should every system administrator possess the ability to alter financial permissions simply because that administrator maintains the underlying technology.
These distinctions are familiar to banking risk management. They are becoming increasingly important as digital-asset infrastructure develops more sophisticated custody, treasury, and settlement services.
The objective is not to make every transaction reversible.
It is to avoid making every compromised credential potentially catastrophic.
AI Defense Is Advancing, but It Cannot Replace Authority
Technology providers are beginning to respond to the acceleration in cyber risk.
In September, OpenAI announced Daybreak for Frontline Defenders, committing $1 billion in subsidized access, training, technical support, and partnerships for organizations protecting essential services.
The initiative includes community and regional banks, critical infrastructure operators, public institutions, and open-source maintainers. Its stated capabilities include examining code, validating vulnerabilities, prioritizing risks, and developing and testing fixes. OpenAI
The announcement illustrates how defensive AI is moving from occasional software analysis toward more continuous security operations.
Yet finding a vulnerability and repairing it are not the same as controlling financial authority.
An AI system might identify an abnormal transaction, flag a suspicious approval request, or recognize that a transfer differs sharply from established behavior.
Whether that warning prevents a loss depends on the institution’s operating rules.
Can the system stop the transfer? Does it require human confirmation? Who is permitted to override the warning? What happens if the monitoring system itself becomes unavailable or compromised?
Those are governance and engineering decisions, not simply model-capability questions.
Giving defensive AI unrestricted power to interrupt financial activity could introduce another vulnerability: a malfunctioning or manipulated system might block legitimate transactions at scale.
Effective automation therefore requires clearly defined permissions, independent oversight, and recovery procedures.
The financial institution remains responsible for deciding what the machine is authorized to do.
The Risk of Shared Defenses
There is another complication.
Financial institutions increasingly rely on common technology providers for cloud computing, security monitoring, identity management, and software development.
AI could make those shared services more capable. It could also increase the consequences of a weakness in one of them.
If numerous banks or exchanges depend on the same provider to identify threats or authorize security responses, an outage or compromise may affect several institutions at once.
Both the IMF and BIS have identified technology concentration and third-party dependencies as important dimensions of emerging financial cyber risk. IMF eLibrary+1
That does not mean every institution should build its own AI security infrastructure.
Smaller organizations may benefit substantially from specialized providers that can deliver capabilities they could not afford independently.
But outsourcing a security function does not eliminate the institution’s exposure to its failure.
Financial resilience increasingly depends on understanding where authority resides across internal systems, vendors, custodians, and payment networks.
A highly capable security service is less reassuring if an institution has no independent means of controlling its most consequential transactions when that service fails.
A Different Measure of Financial Security
The coming cybersecurity contest will involve machines searching for vulnerabilities and other machines attempting to identify and repair them first.
That competition is already changing the economics of software security.
But financial institutions cannot base their resilience entirely on winning every contest over access.
Some intrusions will succeed. Some vulnerabilities will remain undiscovered until they are exploited. Some authorized users will be deceived into approving actions they did not intend.
The institutional question is what those failures are allowed to become.
A compromised employee account should not automatically confer treasury authority. A vulnerable application should not necessarily expose every asset held by a custodian. A failure in one payment service should not have unrestricted consequences for an entire financial network.
Achieving those outcomes requires more than faster vulnerability discovery.
It requires carefully distributed authority, transaction-level controls, independent monitoring, and credible recovery arrangements.
For decentralized finance, those protections must also be weighed against the promise of permissionless execution. For banks and exchanges, they must be reconciled with operating costs, customer access, regulatory obligations, and the speed expected of modern markets.
There will be no single architecture suitable for every institution.
The IMF’s emphasis on limiting the consequences of breaches suggests a useful direction: financial security must be evaluated not only by how effectively an institution resists intrusion, but also by how well it contains the damage when prevention fails.
Artificial intelligence is shortening the time available to respond.
The more durable defense may be to ensure that a successful intrusion does not automatically become permission to move the money.
At CoinEpigraph, we are committed to delivering digital-asset journalism with clarity, accuracy, and uncompromising integrity. Our editorial team works daily to provide readers with reliable, insight-driven coverage across an ever-shifting crypto and macro-financial landscape. As we continue to broaden our reporting and introduce new sections and in-depth op-eds, our mission remains unchanged: to be your trusted, authoritative source for the world of crypto and emerging finance.
— Ian Mayzberg, Editor-in-Chief
The team at CoinEpigraph.com is committed to independent analysis and a clear view of the evolving digital asset order.
To help sustain our work and editorial independence, we would appreciate your support of any amount of the tokens listed below. Support independent journalism:
BTC: 3NM7AAdxxaJ7jUhZ2nyfgcheWkrquvCzRm
SOL: HxeMhsyDvdv9dqEoBPpFtR46iVfbjrAicBDDjtEvJp7n
ETH: 0x3ab8bdce82439a73ca808a160ef94623275b5c0a
XRP: rLHzPsX6oXkzU2qL12kHCH8G8cnZv1rBJh TAG – 1068637374
SUI – 0xb21b61330caaa90dedc68b866c48abbf5c61b84644c45beea6a424b54f162d0c
and through our Support Page.
🔍 Disclaimer: CoinEpigraph is for entertainment and information, not investment advice. Markets are volatile — always conduct your own research.
COINEPIGRAPH™ does not offer investment advice. Always conduct thorough research before making any market decisions regarding cryptocurrency or other asset classes. Past performance is not a reliable indicator of future outcomes. All rights reserved | 版权所有 ™ © 2024-2029.