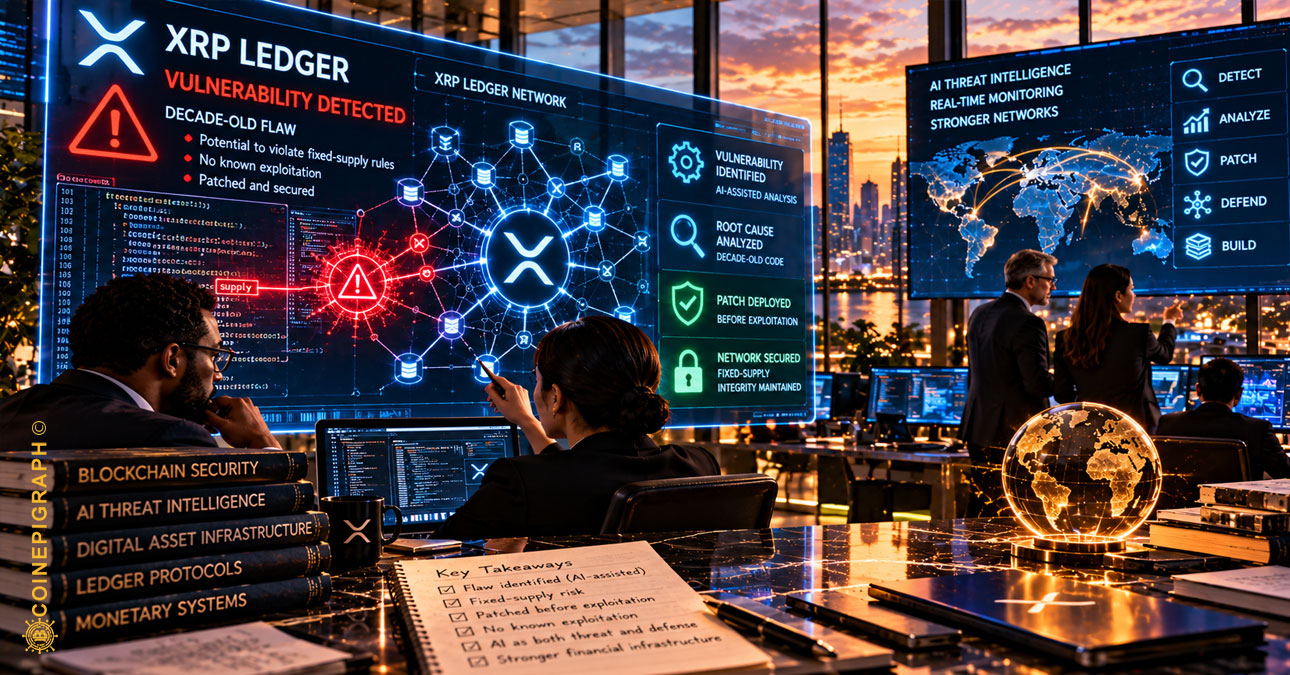
An AI-assisted security investigation uncovered a decade-old XRP Ledger vulnerability capable of violating the network’s fixed-supply rules. The flaw was patched before any known exploitation, but its discovery points toward a larger shift: artificial intelligence is becoming both an attack surface and a defensive instrument for digital financial infrastructure.
By CoinEpigraph Editorial Desk
For more than a decade, a vulnerability sat inside the machinery responsible for moving value across the XRP Ledger.
It was not a stolen private key. It was not a compromised wallet or malicious smart contract. The flaw existed deeper in the protocol—in arithmetic used by the ledger’s payment engine.
Under carefully constructed conditions, an attacker could have exploited an integer overflow while processing multiple offers and caused the ledger to create spendable XRP without the corresponding amount being deducted from the payer. The vulnerability dated to 2015.
It was discovered in September 2026 by an artificial-intelligence agent developed by security firm Veria Labs.
XRP Ledger developers subsequently patched the vulnerability in xrpld version 3.4.1. According to the network’s disclosure, there is no evidence that the flaw was exploited on a public network. Veria reported the vulnerability on September 22, and the patched software was released three days later.
The incident avoided becoming a financial crisis.
What it may have become instead is an early demonstration of how artificial intelligence could change the economics of securing decentralized financial infrastructure.
The Vulnerability Was in the Monetary Machinery
The severity of the flaw came from what it potentially violated.
XRP was created with a fixed initial supply of 100 billion tokens. Transaction fees gradually reduce that amount because XRP used for fees is destroyed.
The vulnerability created a theoretical path around that monetary constraint.
According to the disclosure, an attacker could have created hundreds of deliberately abnormal offers involving tiny quantities of one asset priced against enormous quantities of XRP. A specially constructed payment consuming those offers could cause arithmetic used by the payment engine to overflow.
Instead of recognizing the enormous total being transferred, the calculation could wrap around into a much smaller number.
That mattered because another calculation intended to prevent the creation of unauthorized XRP suffered from a related weakness.
Combined, the flaws created the possibility that sellers would receive their enormous XRP payments while the account initiating the transaction would be charged only a comparatively tiny amount. The attack required deliberate preparation and could not have occurred accidentally.
Veria Labs estimated that its proof of concept could have created approximately 18.45 trillion XRP in a single transaction—more than 180 times the cryptocurrency’s original supply.
That number requires context.
It does not represent XRP that was actually created, nor does it represent a realizable financial loss. Injecting trillions of unauthorized tokens into a market would radically alter the value of the asset itself.
The important point is architectural rather than monetary.
The vulnerability could have violated the ledger’s own rules governing scarcity.
Eleven Years Is the More Interesting Number
The 18 trillion figure makes the headline.
The more consequential number may be eleven.
Code associated with the vulnerability had been present since 2015, surviving years of operation, development and security scrutiny before the flaw was identified.
That does not necessarily mean previous auditors were negligent. Complex financial software can contain interactions that are difficult to identify because individual pieces of code may appear harmless when examined separately.
Veria’s researchers believe this was part of the difficulty. The exploit combined weaknesses whose significance became much greater when used together.
This is precisely where AI-assisted security testing could become important.
Traditional software auditing is constrained by human attention. Researchers determine which paths deserve examination, construct possible attack scenarios and work through combinations of system states.
Artificial intelligence potentially changes the scale of that search.
A sufficiently capable system can inspect code, propose unusual interactions, generate adversarial scenarios and attempt combinations that would be uneconomical for humans to examine manually.
It does not make human security researchers obsolete.
It gives them a different kind of instrument.
AI Changes Both Sides of the Security Equation
That instrument will not belong exclusively to defenders.
The same capabilities that allow an AI system to inspect open-source financial software for previously overlooked vulnerabilities can potentially be used by attackers.
This creates an uncomfortable symmetry.
AI can lower the cost of finding vulnerabilities.
It can lower that cost for everyone.
RippleX engineer Mayukha Vadari acknowledged the changing environment following disclosure of the vulnerability, while XRP Ledger engineering leadership has indicated that AI-assisted bug hunting and formal verification will become more important to its security approach.
That has implications far beyond XRP.
Public blockchains deliberately expose enormous portions of their infrastructure for inspection. Open-source development allows independent researchers to examine software, verify changes and identify vulnerabilities.
AI dramatically increases the potential population of those researchers—but it also increases the potential population of automated adversaries.
The security assumption therefore changes.
It may no longer be sufficient to believe that a vulnerability is safe because sophisticated human researchers have not found it.
Machines can search differently.
The Patch Created Another Governance Problem
The XRP Ledger incident also exposed tension between transparent governance and emergency security.
Ordinarily, significant XRP Ledger rule changes pass through an amendment process requiring sustained validator support.
That process was effectively too slow for this vulnerability.
Once a patch became public, an attacker equipped with AI-assisted code analysis might have been able to identify what had changed, reconstruct the underlying vulnerability and attempt exploitation before the normal amendment process completed.
Developers therefore distributed the security fix without waiting for the usual amendment procedure. More than 80% of validators on the default Unique Node List were reportedly running the patched software by September 25.
That decision raises a difficult infrastructure question.
Decentralized systems value transparency because no central authority should quietly determine the rules.
Security sometimes demands secrecy because revealing the problem before enough infrastructure has been patched can reveal the attack.
Artificial intelligence compresses the time between those two conditions.
A code change that might once have required days of expert analysis to reverse-engineer could potentially be interpreted much faster by automated systems.
The result may be a growing conflict between open governance and coordinated emergency response.
Bug Bounties May Need New Economics
Veria Labs received the XRP Ledger program’s maximum $250,000 bounty for reporting the vulnerability.
That payment has already generated debate. Blockchain investigator ZachXBT argued that the reward was too small relative to the potential severity of the exploit.
The criticism points toward another emerging problem.
If AI dramatically increases the rate at which valuable vulnerabilities can be discovered, protocols will need economic systems capable of directing that capability toward responsible disclosure rather than exploitation.
Bug bounties are therefore more than compensation for researchers.
They are incentive infrastructure.
The calculation becomes particularly important when an AI-assisted researcher discovers a vulnerability that could theoretically produce far more value through exploitation than through disclosure.
Protocols may eventually find themselves competing for defensive AI talent in much the same way technology companies compete for cybersecurity researchers today.
From Code Audits to Continuous Adversaries
Blockchain security has traditionally relied on audits performed before deployment, bug-bounty programs after deployment and human researchers continuously examining systems from the outside.
AI could make that model more persistent.
Instead of commissioning an audit and receiving a report, a protocol could eventually operate AI systems continuously attempting to break its own assumptions.
They could probe transaction combinations, search for arithmetic edge cases, examine proposed upgrades and construct adversarial behavior before new code reaches production.
The distinction is important.
An audit examines software.
An automated adversary continually challenges it.
That may become increasingly necessary as AI gives potential attackers the same capabilities.
The XRP Ledger vulnerability did not become the catastrophic monetary event it could theoretically have produced. No evidence currently indicates that unauthorized XRP was created on a public network.
But the incident revealed something potentially more durable than the flaw itself.
Artificial intelligence is beginning to participate directly in the security of financial infrastructure—not simply monitoring transactions after something goes wrong, but examining the machinery that determines whether those transactions are possible in the first place.
For blockchain networks, the coming security contest may therefore involve machines searching for weaknesses while other machines search for them first.
The AI security race is not approaching digital finance from the outside.
It has already entered the code.
At CoinEpigraph, we are committed to delivering digital-asset journalism with clarity, accuracy, and uncompromising integrity. Our editorial team works daily to provide readers with reliable, insight-driven coverage across an ever-shifting crypto and macro-financial landscape. As we continue to broaden our reporting and introduce new sections and in-depth op-eds, our mission remains unchanged: to be your trusted, authoritative source for the world of crypto and emerging finance.
— Ian Mayzberg, Editor-in-Chief
The team at CoinEpigraph.com is committed to independent analysis and a clear view of the evolving digital asset order.
To help sustain our work and editorial independence, we would appreciate your support of any amount of the tokens listed below. Support independent journalism:
BTC: 3NM7AAdxxaJ7jUhZ2nyfgcheWkrquvCzRm
SOL: HxeMhsyDvdv9dqEoBPpFtR46iVfbjrAicBDDjtEvJp7n
ETH: 0x3ab8bdce82439a73ca808a160ef94623275b5c0a
XRP: rLHzPsX6oXkzU2qL12kHCH8G8cnZv1rBJh TAG – 1068637374
SUI – 0xb21b61330caaa90dedc68b866c48abbf5c61b84644c45beea6a424b54f162d0c
and through our Support Page.
🔍 Disclaimer: CoinEpigraph is for entertainment and information, not investment advice. Markets are volatile — always conduct your own research.
COINEPIGRAPH™ does not offer investment advice. Always conduct thorough research before making any market decisions regarding cryptocurrency or other asset classes. Past performance is not a reliable indicator of future outcomes. All rights reserved | 版权所有 ™ © 2024-2029.