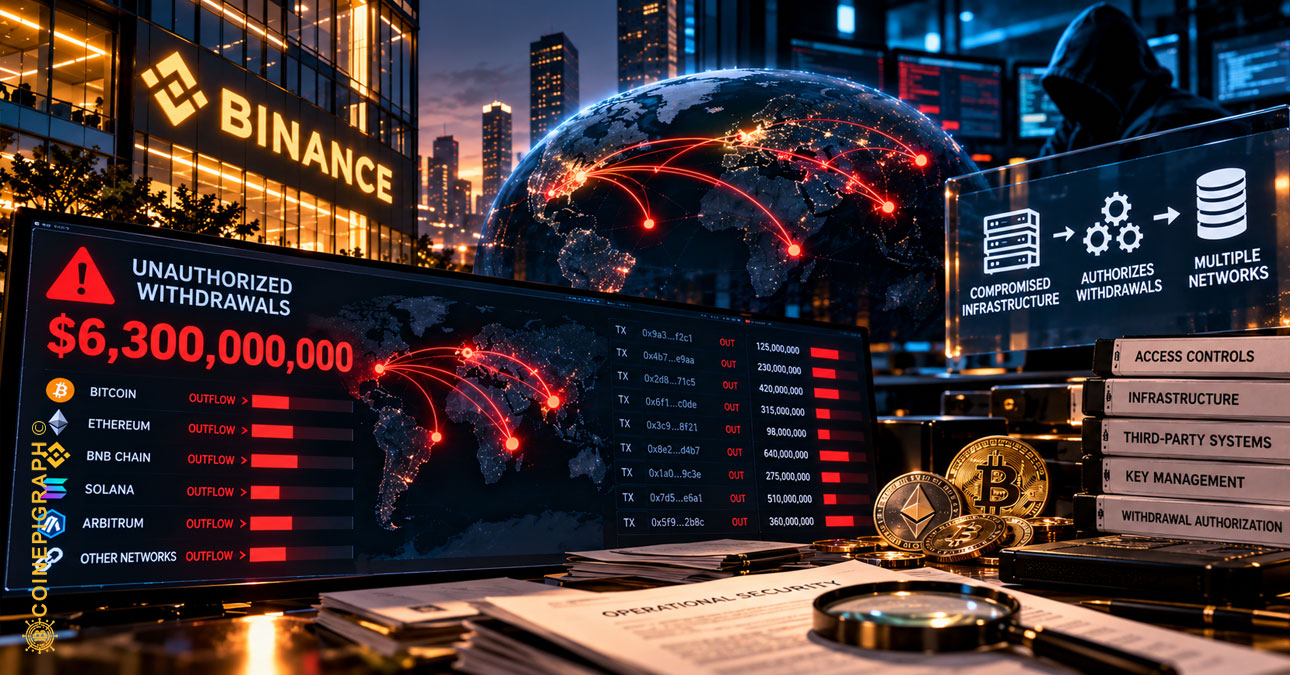
Approximately $6.3 billion was stolen from Binance after attackers compromised infrastructure capable of authorizing withdrawals across multiple networks. Binance says there is no evidence its private keys leaked. The largest theft in crypto history is exposing a more difficult security problem: protecting the machinery trusted to use the keys.
By CoinEpigraph Editorial Desk
The largest known theft in cryptocurrency history may ultimately be remembered for something other than its size.
The blockchain did not have to break.
Beginning shortly after 20:00 UTC on October 29, attackers drained approximately $6.3 billion in digital assets from hot wallets operated by Binance, the world’s largest cryptocurrency exchange. Most of the theft unfolded in roughly 20 minutes. Bitcoin, Ether, stablecoins and other assets moved across multiple blockchain networks before Binance suspended withdrawals and began trying to contain the damage.
By Friday, approximately $3 billion of affected assets had been frozen onchain. Binance said it had set aside more than $6.34 billion from its corporate resources and Secure Asset Fund for Users to absorb the losses, with roughly $5 billion already held in the same assets that were stolen. Customers, the exchange says, will not bear the financial loss.
The numbers alone make the event historic.
But the more consequential question is how the money moved.
Binance initially said its investigation suggested that a DevOps engineer’s laptop had been compromised, allowing an attacker to reach an internal service container and initiate unauthorized withdrawals. The company has since cautioned that investigators have discovered additional points of breach.
The complete attack sequence remains under investigation.
One finding, however, has remained notable: Binance says it has found no evidence that its wallet private keys were leaked.
If that conclusion survives the forensic investigation, the attack exposes a security problem extending far beyond one exchange.
The attacker may not have needed to steal the key.
It may have been enough to compromise the machinery trusted to use it.
The Vault Key Was Not Necessarily the Target
Cryptocurrency security has traditionally placed extraordinary emphasis on private keys.
That makes sense. A private key authorizes control over a blockchain address. Lose it and the assets associated with it can often be moved irreversibly.
Exchanges consequently separate large reserves into cold storage while maintaining smaller pools in internet-connected hot wallets to process withdrawals and other routine transactions. Security systems surround the signing process with access controls, authorization policies and operational procedures intended to prevent a single compromised machine or employee from moving enormous amounts of money.
The Binance attack is testing that architecture.
According to the exchange’s preliminary findings, the attacker penetrated operational infrastructure capable of submitting unauthorized withdrawal transactions. Blockchain investigators examining the incident have described the attack more broadly as a compromise of transaction-signing infrastructure.
That distinction matters.
Stealing a cryptographic key and compromising a system authorized to instruct that key are different attacks.
The first defeats the cryptography directly.
The second defeats the institution surrounding it.
In both cases, the blockchain can receive a transaction that appears cryptographically valid.
That may be one of the most important lessons emerging from the incident.
Blockchain networks are exceptionally good at determining whether a transaction contains the authorization required by their protocols. They are not necessarily capable of determining whether the institution producing that authorization intended to produce it.
One Ethereum Wallet Shows How the Problem Worked
The Ethereum portion of the attack provides an unusually visible example.
Investigators say an attacker used EIP-7702, an Ethereum feature introduced in 2025 that allows an externally owned account to delegate execution to smart-contract code.
The feature itself was not the root compromise.
Something more fundamental had to happen first: the attacker needed valid authorization.
According to analyses of the onchain transactions, approximately 50 authorization attempts were prepared against one Binance hot wallet, commonly identified as Binance 14. Most failed. One succeeded.
That successful authorization allowed malicious code to exercise control over the account and sweep assets from it.
The second source transcript describes the same pattern: multiple authorizations were prepared against changing transaction nonces until one matched, after which the malicious execution system could drain the wallet.
Approximately $2.5 billion was removed through the Ethereum wallet in minutes.
The malicious delegation reportedly remained active afterward, creating another problem. As automated Binance systems continued moving assets through the affected operational infrastructure, newly arriving funds could also become exposed.
It is tempting to describe this as an EIP-7702 exploit.
That would miss the larger issue.
EIP-7702 provided a mechanism through which authority could be exercised. It does not yet explain how the attacker obtained the legitimate authorization required to exercise it.
That question remains part of the investigation.
And it is probably more important than the Ethereum feature itself.
The Attack Was Larger Than Ethereum
The theft also crossed blockchain boundaries.
Bitcoin and assets on other networks were removed from Binance-controlled wallets during the same period. Those networks do not use Ethereum’s EIP-7702 mechanism.
That tells investigators something important.
Whatever failed was not confined to one Ethereum wallet.
The second transcript describes Bitcoin and Tron withdrawals occurring during the same attack window and argues that access to the broader withdrawal-approval system could explain why the attacker was able to operate across different networks.
Binance has now said investigators have uncovered additional breach points beyond the initially suspected laptop. It has not yet disclosed the complete architecture of those compromises.
That is why early explanations should remain provisional.
A global forensic effort involving Binance, blockchain intelligence firms, token issuers, exchanges and law enforcement is still reconstructing what happened.
The final technical account may look different from the first one.
Then Centralization Started Recovering the Money
What happened after the theft exposes another dimension of digital-asset architecture.
Stablecoin issuers began freezing stolen assets.
Tether immobilized stolen USDT. Circle acted against USDC. Other issuers and industry participants joined recovery efforts. Binance now says approximately $3 billion of affected assets have been frozen onchain.
That is an extraordinary containment response.
It is also an extraordinary demonstration of control.
Dollar-backed stablecoins may move across decentralized blockchain networks, but major stablecoins generally retain an issuer capable of exercising administrative authority over the token contract. If an address is blacklisted, affected tokens can become impossible to transfer even though the blockchain itself continues operating.
In this incident, that power worked against a thief.
It potentially prevented billions of dollars in stolen assets from being converted, transferred or laundered.
But the architecture does not distinguish philosophically between good freezes and bad ones. It provides an administrative capability, and an institution determines when that capability should be exercised.
The Binance attack therefore demonstrated two forms of centralized authority almost simultaneously.
Centralized operational infrastructure appears to have helped an attacker move assets.
Centralized issuer infrastructure then helped stop some of those assets from moving.
The same incident revealed both the vulnerability and utility of institutional control.
Bitcoin and Ether Behaved Differently
Bitcoin and Ether expose the other side of the architecture.
There is no Bitcoin company with a blacklist function capable of immobilizing stolen BTC.
There is no Ethereum issuer capable of remotely freezing ETH at a particular address.
Once those native assets have moved to an address controlled by an attacker, recovering them becomes considerably more difficult. Authorities and investigators can trace the assets. Exchanges can refuse deposits associated with known stolen funds. Law enforcement can seize private keys if it obtains them.
But nobody can simply instruct the Bitcoin or Ethereum protocol to freeze the coins.
Investigators estimate that billions of dollars in stolen Bitcoin and Ether may consequently remain beyond the immediate reach of the recovery effort.
The distinction reveals something important about digital property.
The ability to recover an asset after theft depends partly upon where authority resides in the architecture.
Stablecoins sacrifice some absolute bearer-like independence in exchange for an administrative layer that can intervene.
Native decentralized assets remove much of that administrative authority, but the same characteristic makes unauthorized transfers much harder to reverse.
Neither architecture eliminates risk.
They distribute it differently.
Binance Can Absorb the Loss
The financial consequences also distinguish this event from earlier exchange failures.
Binance says it will absorb the entire loss rather than impose it on customers.
The company has already reserved more than $6.34 billion for the response and says approximately 80% of the affected assets have effectively been matched with equivalent corporate holdings. It is acquiring the remainder through market and over-the-counter transactions.
That matters because the history of cryptocurrency is filled with security incidents that became solvency events.
A stolen asset does not merely disappear from an exchange’s wallet. If the exchange owes that asset to a customer, the liability remains.
The question then becomes whether the institution has sufficient resources to replace what was lost.
Binance appears to be attempting exactly that.
Its size may prevent the largest theft in crypto history from becoming one of crypto’s largest customer-loss events.
But that should not obscure what happened operationally.
A financial institution capable of absorbing a $6.3 billion security loss is still a financial institution that suffered a $6.3 billion security loss.
Balance-sheet strength can absorb the consequence.
It cannot explain the breach.
Attribution Remains Unfinished
Several blockchain intelligence firms have identified characteristics resembling previous attacks attributed to North Korean hacking operations.
TRM Labs has expressed high confidence in a North Korean connection, drawing comparisons with the 2025 Bybit attack, which the FBI attributed to North Korean actors.
Binance itself has not reached that conclusion publicly.
Nor had law enforcement publicly confirmed responsibility as this article was prepared.
That distinction matters.
The identity of the attacker may ultimately become an important part of the story, particularly if the incident proves to be another example of state-linked actors targeting the operational infrastructure surrounding digital assets.
But attribution should follow evidence.
For now, the attack mechanism matters even without knowing who operated it.
Crypto Security Is Moving Beyond the Key
The cryptocurrency industry has spent more than a decade improving how private keys are generated, stored and protected.
Cold storage moved keys away from internet-connected systems.
Hardware wallets isolated signing operations.
Multisignature systems distributed authorization.
Multiparty computation divided signing authority among multiple systems so that no single machine necessarily possessed a complete private key.
Those developments remain important.
But institutional digital finance introduces another problem.
A private key rarely operates alone.
Software requests transactions. Employees administer systems. Cloud infrastructure connects services. Policy engines decide whether transactions satisfy internal rules. Signing systems authorize execution. Wallet software constructs messages. Networks broadcast them.
Every component creates another place where intent must remain aligned with authorization.
The Binance attack appears to have entered somewhere inside that machinery.
That makes the incident relevant far beyond cryptocurrency exchanges.
Banks are developing digital-asset custody.
Traditional securities are moving onchain.
Stablecoins are entering payment infrastructure.
Institutional wallets are becoming treasury systems.
Financial institutions increasingly need software capable of initiating blockchain transactions automatically and at enormous scale.
The more financial infrastructure becomes programmable, the more security must protect not only the asset and the cryptographic key, but also the systems capable of telling that key what to do.
The Blockchain Did What It Was Told
There is an uncomfortable simplicity beneath the largest crypto theft on record.
Bitcoin did not have to fail.
Ethereum did not have to stop producing blocks.
Cryptographic signatures did not necessarily have to be broken.
The networks processed transactions according to their rules.
The apparent failure occurred somewhere between human intention and cryptographic authorization.
That boundary is becoming increasingly important as digital finance becomes institutional.
For years, one of cryptocurrency’s foundational security principles could be reduced to possession of the private key.
The Binance attack suggests that principle is no longer sufficient for institutions controlling billions of dollars through complex automated systems.
The next generation of digital-asset security will have to answer a harder question.
It is not merely who possesses the key.
It is who controls the machinery trusted to use it.
Editor’s note: This article reflects verified information available on October 30, 2026. Binance’s forensic investigation remains active, and the exchange says additional breach points have been identified beyond its initial findings. CoinEpigraph will revisit the incident when the complete technical post-mortem and independent forensic findings become available.
At CoinEpigraph, we are committed to delivering digital-asset journalism with clarity, accuracy, and uncompromising integrity. Our editorial team works daily to provide readers with reliable, insight-driven coverage across an ever-shifting crypto and macro-financial landscape. As we continue to broaden our reporting and introduce new sections and in-depth op-eds, our mission remains unchanged: to be your trusted, authoritative source for the world of crypto and emerging finance.
— Ian Mayzberg, Editor-in-Chief
The team at CoinEpigraph.com is committed to independent analysis and a clear view of the evolving digital asset order.
To help sustain our work and editorial independence, we would appreciate your support of any amount of the tokens listed below. Support independent journalism:
BTC: 3NM7AAdxxaJ7jUhZ2nyfgcheWkrquvCzRm
SOL: HxeMhsyDvdv9dqEoBPpFtR46iVfbjrAicBDDjtEvJp7n
ETH: 0x3ab8bdce82439a73ca808a160ef94623275b5c0a
XRP: rLHzPsX6oXkzU2qL12kHCH8G8cnZv1rBJh TAG – 1068637374
SUI – 0xb21b61330caaa90dedc68b866c48abbf5c61b84644c45beea6a424b54f162d0c
and through our Support Page.
🔍 Disclaimer: CoinEpigraph is for entertainment and information, not investment advice. Markets are volatile — always conduct your own research.
COINEPIGRAPH™ does not offer investment advice. Always conduct thorough research before making any market decisions regarding cryptocurrency or other asset classes. Past performance is not a reliable indicator of future outcomes. All rights reserved | 版权所有 ™ © 2024-2029.